
Radar: Free Email Security Health Check by Mailprotector
Radar by Mailprotector is a free email security health check tool that helps organizations gain full visibility into all services sending email from their clients' domains, manage and authenticate senders through SPF, DKIM, DMARC, and BIMI configurations, and achieve full DMARC enforcement (p=reject) within about 90 days by providing analysis, implementation guidance, and compliance tracking all within a single platform.
Close the loop on email health.
DMARC management and more, giving you a complete picture of who is sending from your clients' domains, what to fix, and how to prove it's working.
From exposed to enforced, in three phases.
Microsoft 365
Enforced ✓
HubSpot
Enforced ✓
Salesforce
Enforced ✓
Mailchimp
Enforced ✓
relay.cheapvpshost.net
Blocked
mta2.bulk-blaster.io
Blocked
Forwarder
Enforced ✓
203.0.113.47
Blocked
Zendesk
Enforced ✓
DocuSign
Enforced ✓
p=reject
Phase 1: Analyze
See who is using your clients' domains.
Add a single DNS record and Radar gets to work. Within days you have a full map of every service sending email from your clients' domains: the authorized tools, the shadow IT, the forwarders, and anything that looks suspicious. Most organizations are surprised by what shows up.
Phase 2: Implement
Get every sender authenticated.
With the full picture in front of you, Radar makes it straightforward to fix what's broken and configure what's missing. Manage SPF records, DKIM keys, DMARC policy, and BIMI from one tool. A shareable setup link lets you hand off DNS tasks to whoever owns the records, with self-verification built in so you know when it's done.
Phase 3: Enforce
Reach p=reject. Show your work.
The real goal is full enforcement. Radar tracks compliance across every authorized sender, surfaces what's still failing, and helps you keep your clients on a clear path forward. Most organizations get to p=reject within 90 days. Radar gives you the reports to check every step.
Everything email authentication requires in one platform
The Dashboard
Full visibility, zero guesswork
The Radar dashboard gives you a high-level view of each domain's authentication health at a glance. See DMARC policy status, email volume, sender compliance, and any issues that need attention. Switch between clients in a click without leaving the platform.
 Radar™
- Dashboard
- Reports
- Domains
- Alerts
- Activity Logs
ACAcme Corp
Dashboard
Overview of DMARC reporting for domains and senders
09/07/2026 - 10/07/2026(UTC)
Domains
1 Reporting
1 Total
View Domains
0%Enforced
Email volume
41.8K Approved
1.5K Unapproved & other
Senders
5 Approved
12 Unapproved
View Senders
29%Approved
Domains
Volume
Approved
Unapproved
a
acmecorp.com
none
43,323
5
Senders
41.8K
Volume
99%
12
Senders
1.5K
Volume
0%
View Report
Passing DMARCFailing DMARCForwards
View All Domains
Approved Senders by Volume
Volume
Compliance
Domain
Microsoft Exchange Online
Mailbox Provider
15,294
100%
acmecorp.com
M
Marketo
Sales & Marketing
14,763
100%
acmecorp.com
Amazon SES
Transactional Mail
8,117
100%
acmecorp.com
SendGrid
Transactional Mail
3,203
100%
acmecorp.com
Mailchimp
Sales & Marketing
416
100%
acmecorp.com
Passing DMARCFailing DMARCForwards
All SendersApprovedForwarderUnapprovedSuspiciousNone
Compliance
41,377
/ 43,323
95.5%Compliant
Email Volume
43,323
- Forwards (1,301)
- Passing DMARC (41,377)
- Failing DMARC (645)
Senders
17
IP Addresses (34)
Search
Passing DMARCFailing DMARCForwards
Sender
Compliance
Volume
Category
Microsoft Exchange Online
Mailbox Provider
100%
15,294
Approved
M
Marketo
Sales & Marketing
100%
14,763
Approved
Amazon SES
Transactional Mail
100%
8,117
Approved
SendGrid
Transactional Mail
100%
3,203
Approved
C
Cloudmark
Mailbox Provider
100%
638
Forwarder
Mailchimp
Sales & Marketing
100%
416
Approved
T
Tokai Japan
ISP
100%
79
Suspicious
12
Sender Intelligence
Know every sender by name
Radar identifies and categorizes every service sending from a client's domain: authorized senders, email forwarders, unapproved tools, and anything that looks like spoofing activity. You see the compliance rate for each one, and can drill into individual IP addresses to understand exactly what is happening and why.
Policy Management
DMARC, SPF, and DKIM in one place
Manage all four authentication layers from a single interface without switching between DNS providers and configuration files. DMARC policy updates happen with a click. SPF flattening keeps records valid as cloud services accumulate. DKIM key management imports known selectors automatically.
DMARCSPFDKIM
Verified, Reporting- Last Checked on 10-06-2026 02:00
VerifySetup Instructions
Policy Settings
DMARC is the email policy and reporting protocol that controls what happens to email that fails authentication. It helps to ensure that only authorized parties can send email from the domain. What's new in DMARCbis
DMARC Policy
NoneQuarantineReject
Subdomain Policy
InheritNoneQuarantineReject
Non-Existent Subdomain DMARC Policy New DMARCbis
InheritNoneQuarantineReject
Testing Mode New DMARCbis
NoYes
Percentage Legacy
100%
Aggregate Reports
Failure Reports
Alignment Settings
View Raw DMARC Record
CancelSaveSave and Back
Verified, Flattened- 4 of 10 lookups used
VerifySetup Instructions
Authorized Senders
Configure which domains and services are authorized to send email on behalf of your domain.
Add New SPF DirectiveImportView SPF Tree
#QualifierTypeAddress ValueLookups
1PassInclude
Microsoft Corporation
spf.protection.outlook.com
1 Lookup
2PassInclude
HubSpot
spf.hubspot.com
2 Lookups
3PassInclude
SendGrid
sendgrid.net
1 Lookup
Default Qualifier
SPF Flattening
Compress includes to raw IP addresses automatically so the record stays under the 10-lookup limit regardless of how many services the domain uses.
EnabledDisabled
View Raw SPF Record
CancelSaveSave and Back
Verified, 3 Keys Active- Last Checked on 10-06-2026 02:00
VerifySetup Instructions
DKIM Keys
DKIM adds a digital signature to outgoing mail so receivers can confirm it was not altered in transit. Known selectors for your sending services are imported automatically.
Generate KeyImport Selector
SelectorServiceKeyStatus
selector1._domainkeyMicrosoft 3652048-bitActive
hs1-12345._domainkeyHubSpot2048-bitActive
s1._domainkeySendGrid1024-bitActive
k1._domainkeyMailchimp2048-bitPending
Key Rotation
Alignment Settings
View Raw DKIM Records
CancelSaveSave and Back
Domain Report
acmecorp.com
a
63%
Domain Score
Moderate Risk
You have implemented some measures to protect recipients from malicious emails sent from your domain. However, attention should be given to areas where controls can be strengthened. These measures help build trust in your organization, protect recipients from attacks, and ensure effective email deliverability.
Impersonation
3/5
One more change is needed to fully protect your domain. Savvy cybercriminals could still impersonate your business and stakeholders. Deliverability of legitimate email may be disrupted and some messages may land in Spam or Junk folders.
Branding
0/5
Right now, your branding isn't displayed with your emails. Branding builds trust and assures recipi...more
Privacy
2/5
You need to tighten up your email encryption. If it's not secure, your emails could be intercepted.
Reporting
Numbers that make the case
Radar turns raw DMARC data into clean, filterable views. It can help you track compliance rates, email volume, deliverability, and sender reputation over time, across the many domains you manage. Pull the data you need to show customers their progress, justify the service, and open conversations about what email security issues to tackle next.
MTA-STS and TLS-RPT
Inbound security included
Radar also supports MTA-STS and TLS-RPT to enforce encrypted transport for inbound mail and surface any delivery failures. It is a useful complement to DMARC that clients can add as part of the same project or down the road.
MTA-STSTLS-RPT
Mode: enforceLast 14 days
Timeline
1,284 Successful
8 Failed
Top Failure Type
- certificate-host-mismatch (8)
Reported by gmail.com for mx2.acmecorp.com
- No other failures reported over the selected period
View TLS report
BIMI
Put your clients' logo in the inbox
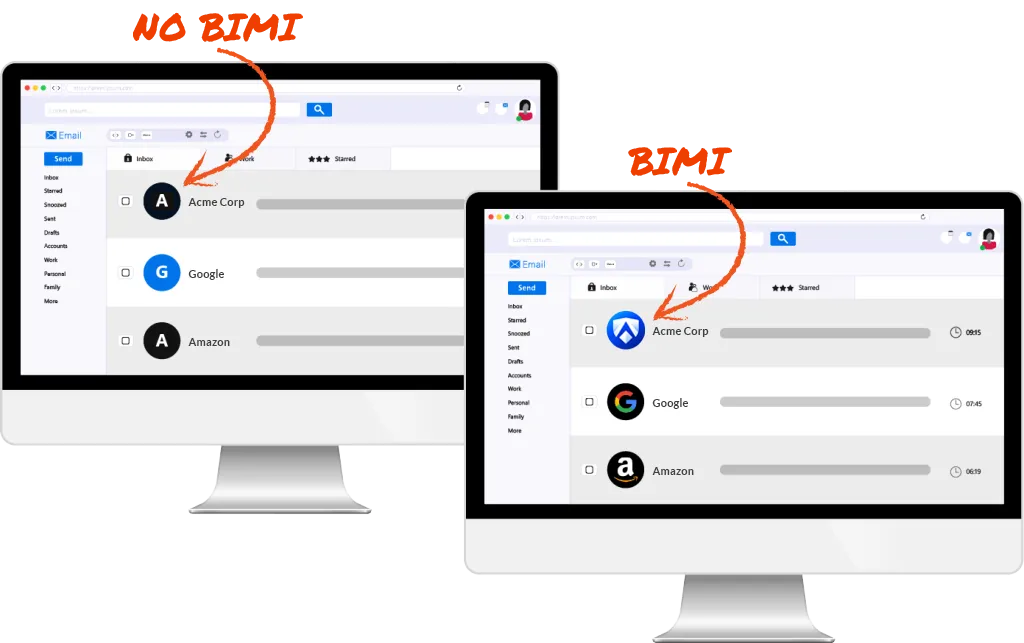
Once DMARC enforcement is in place, BIMI lets clients display their brand logo next to emails in Gmail, Apple Mail, and other supporting providers. Radar tracks which mail providers are recognizing the BIMI certificate, giving you a concrete story to tell about email brand value.
A key email security service your clients need, but a conversation most MSPs aren't having
Most of your clients already have some form of DMARC in place. They may have set it up themselves or relied on a past MSP to get it right. The problem is that the majority are stuck at p=none, which means the record exists but provides no actual protection long term.
Full enforcement is often a service gap, and a significant growth opportunity
Radar gives you a practical way to open the email health conversation
Lead with the problem, let the data do the talking
Run a quick domain analysis for any prospect and Radar immediately surfaces their authentication gaps. It's an easy, visual way to show potential clients exactly where they are vulnerable before you've even had the full security conversation.
A ready-made expansion conversation
DMARC is increasingly required by regulators and major email providers. Radar gives you a concrete, compliance-focused service to add to the conversation for contract renewals or to entice new prospects. It builds on what you already manage and raises the floor of what "protected" actually means.
Explain that the mandate is already here
Your clients may not know that since 2024, Google, Yahoo, and Microsoft have all tightened email authentication requirements. Regulatory frameworks including PCI DSS v4.0, GDPR, and NIST CSF all point toward DMARC as part of a baseline security posture. Your clients are feeling the pressure. Radar is how you help them respond to it.
Put your brand front and center
As clients progress through their DMARC journey, all reports they receive will come branded to your MSP. Every email health update reinforces that your team is the one driving their results. This gives you a natural touchpoint to show the value of what you manage.
From the Trenches
The perfect response to ‘I already have an IT guy’
We've had great success using Radar during discovery conversations. When a prospect doesn't receive a perfect score, it naturally opens the door to a deeper discussion around security gaps, risk exposure, and best practices. Instead of us pitching what might go wrong, Radar gives them something concrete to look at. We've used this approach with our last five prospects, and three of them have moved forward as new managed clients.
Nik Margulski
XTECHS
Radar closes the authentication gap. Mailprotector's filtering covers the rest.
Radar is sold bundled with one of our two popular email filtering products.
 \
Zero Trust Email Security\
\
Shield provides advanced email security that protects your users without slowing down their productivity. Malicious, suspicious, and unwanted mail gets blocked with no complex allow/deny lists and no MX or DNS changes.\
Learn more
 \
Platform Agnostic Email Filtering\
\
The MSP-first secure email gateway built with multi-tenant management in mind. CloudFilter's deep administrative control that doesn't take an email expert to run makes this the perfect tool for complex or custom email environments.\
Learn more
Frequently Asked Questions
What is DMARC and why does it matter now?
DMARC stands for Domain-based Message Authentication, Reporting, and Conformance. It is an email authentication standard that tells receiving mail servers what to do with emails that fail SPF or DKIM checks. Without it, anyone can send an email that appears to come from your domain. Since 2024, Google, Yahoo, and Microsoft have all introduced stricter authentication requirements, and regulators are following. The question for most businesses is no longer whether to implement DMARC, but how quickly they can get to full enforcement.
How is Radar different from other DMARC tools?
Beyond being bundled with Mailprotector tools you already love, some other DMARC tools simply check whether records are present and correctly formatted. Radar goes several steps further: it processes live DMARC data from actual email flows, identifies every service sending from a domain, categorizes senders, and gives you the controls to fix authentication issues and advance policy. It is an ongoing management platform, not a one-time check.
What does getting to p=reject actually involve?
It starts with visibility: understanding every service that sends email from the domain. Then each sender needs to be properly authenticated through SPF alignment, DKIM signing, or both. Once the legitimate senders are covered, you can move the DMARC policy from none to quarantine and eventually to reject. Radar walks you through that progression and tracks compliance at each step. Most clients get there within 90 days.
What does Radar manage beyond DMARC?
Radar handles SPF including automatic SPF flattening to stay under the 10-lookup limit, DKIM key management, DMARC policy, MTA-STS for enforcing encrypted inbound transport, TLS-RPT for transport layer reporting, and BIMI for inbox brand display. Everything a domain needs to be fully authenticated and enforced is in one SKU.
What is SPF flattening?
SPF records have a limit of 10 DNS lookups. Add a handful of cloud services and it is easy to exceed that limit, which causes SPF to silently fail. Radar’s SPF flattening compresses the record into raw IP addresses automatically, keeping the client under the limit regardless of how many services they use.
What happens to my clients' email data?
Radar processes DMARC aggregate reports, which contain metadata about email flows and not the content of individual messages. Message content is never exposed. Forensic failure reports, which can contain more detail, are turned off by default and must be explicitly enabled per domain.
How does Radar fit with the rest of the Mailprotector platform?
Radar is part of the Mailprotector email security suite, so it lives in the same Console your team already uses (or will soon) for email security. DMARC management sits alongside inbound filtering, encryption, and archiving as part of a complete email security offering. No separate vendor, no separate login, no multiple invoices to keep track of, and, most importantly, no gap in coverage.
Ready to add DMARC, DKIM, SPF, and BIMI to your security stack?
Talk to us about getting your clients from exposed to enforced, and see how Radar fits alongside the tools you already use.